

Talos Director is in Limited Availability. Limited Availability customers receive full production support and work directly with Sidero Labs engineering during onboarding. General availability is planned for January 2027, and the console is changing quickly until then, so details on these pages may differ from what you see.To request access, visit siderolabs.com/getdirector.
VM micro-segmentation
The firewall pages live under Network in the console. They are built from two objects: security groups, which decide which VMs a rule applies to, and policies, which hold the rules.Security groups
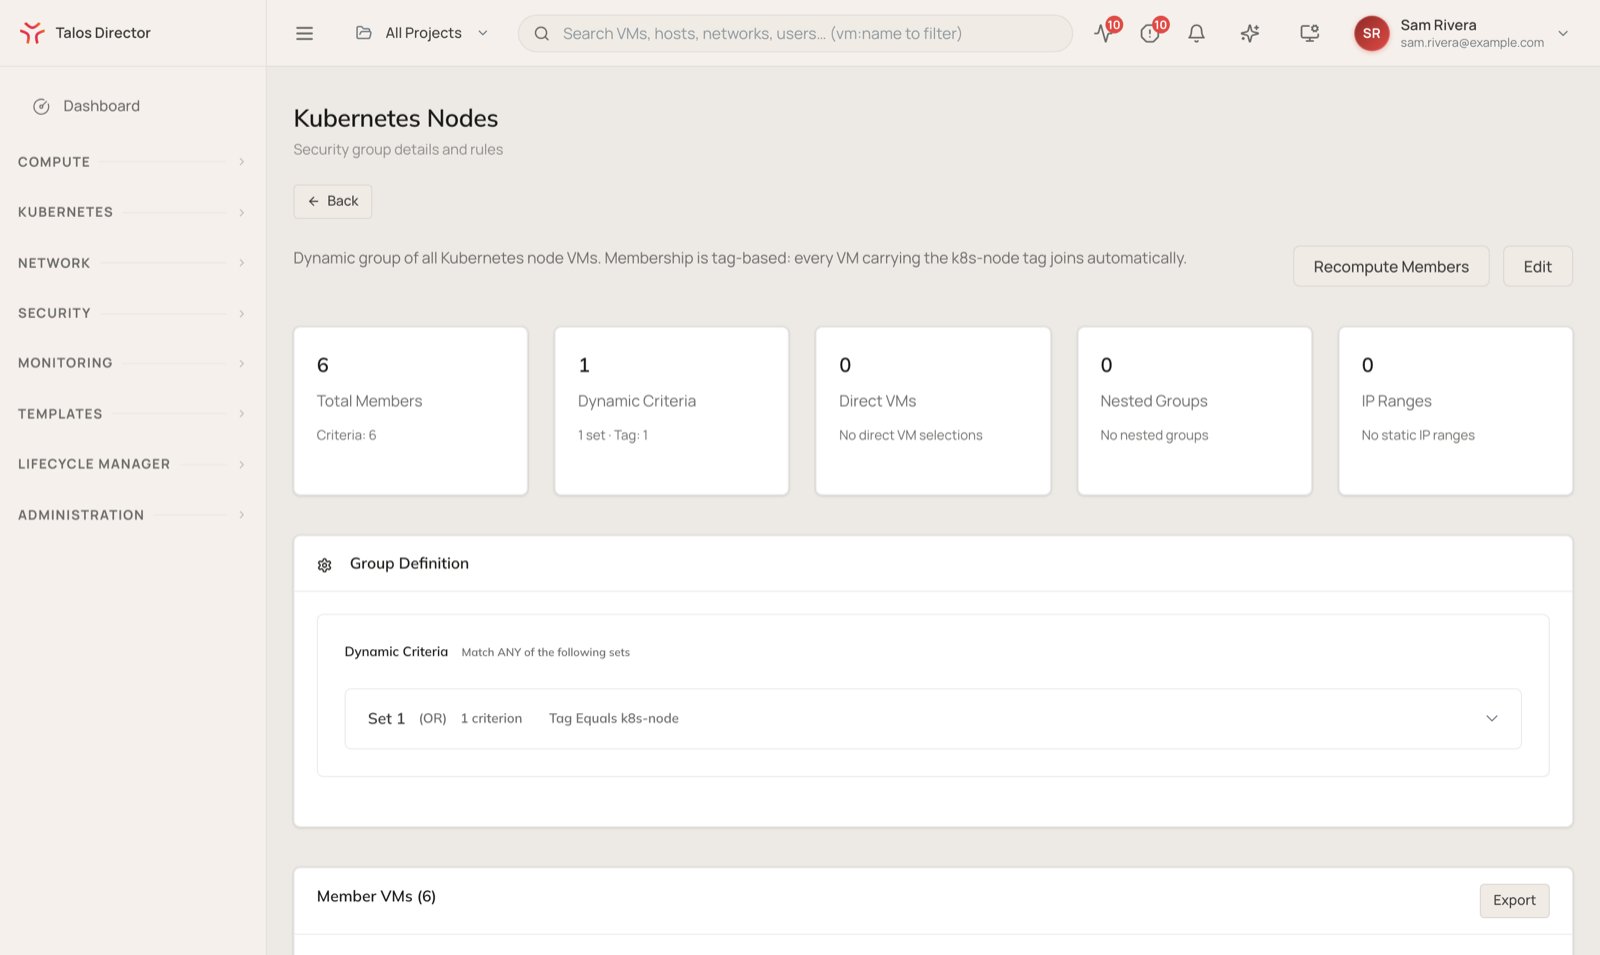
Navigate to Network > Security Groups (/security-groups). A security group is a set of VMs and addresses that policies can refer to by name. Members can come from:
- Dynamic criteria: rules that match VMs, for example every VM with a given tag. Membership updates as VMs are created, tagged, and removed.
- Direct VMs: specific VMs added by hand.
- Nested groups: other security groups.
- IP ranges: static addresses outside Talos Director.
Policies
Navigate to Network > Policies (/policies). Each policy has a priority, a scope (the security groups it applies to), and a set of rules that allow or deny traffic. Policies are evaluated highest priority first. Select Add Policy to create one.
Both the Security Groups and Policies views offer Import from NSX, to bring existing VMware NSX groups and firewall rules across when you move VMs from VMware.
A VM’s Network tab lists every policy applied to it. See The VM detail screen.
Test and observe traffic
- Network > Policy Simulator answers “would this flow be allowed?” before you depend on it. Enter a source and destination (a VM or an IP address), a protocol, and a port, then select Run connectivity test to see the verdict and the rule responsible. The same test is on each VM’s Network tab.
- A VM’s Firewall Activity tab captures the firewall’s live verdicts on that VM’s traffic for a fixed period, so you can see what is being dropped and why.
Kubernetes cluster security
The Security section covers the Kubernetes clusters Talos Director manages. It draws on four sources, each installed as a cluster add-on: CIS benchmark scans (kube-bench), Falco and Tetragon for runtime detection, and Kyverno for admission policy. See Add-ons.
Each cluster’s own Security tab shows the same information for that cluster alone. See The cluster detail screen.